Article 15: Portability
A customer's full profile, contract status and payment method metadata, compiled as a structured export on request.
Security & Compliance
Billing software holds some of the most regulated data a company has: card details, VAT IDs, invoices and personal data under GDPR. Here's specifically how Subscription Billing and E-Invoicing handle each of those.
This page describes the security and compliance tooling built into the products. It isn't a substitute for your own legal review, and we only list certifications we actually hold.
GDPR
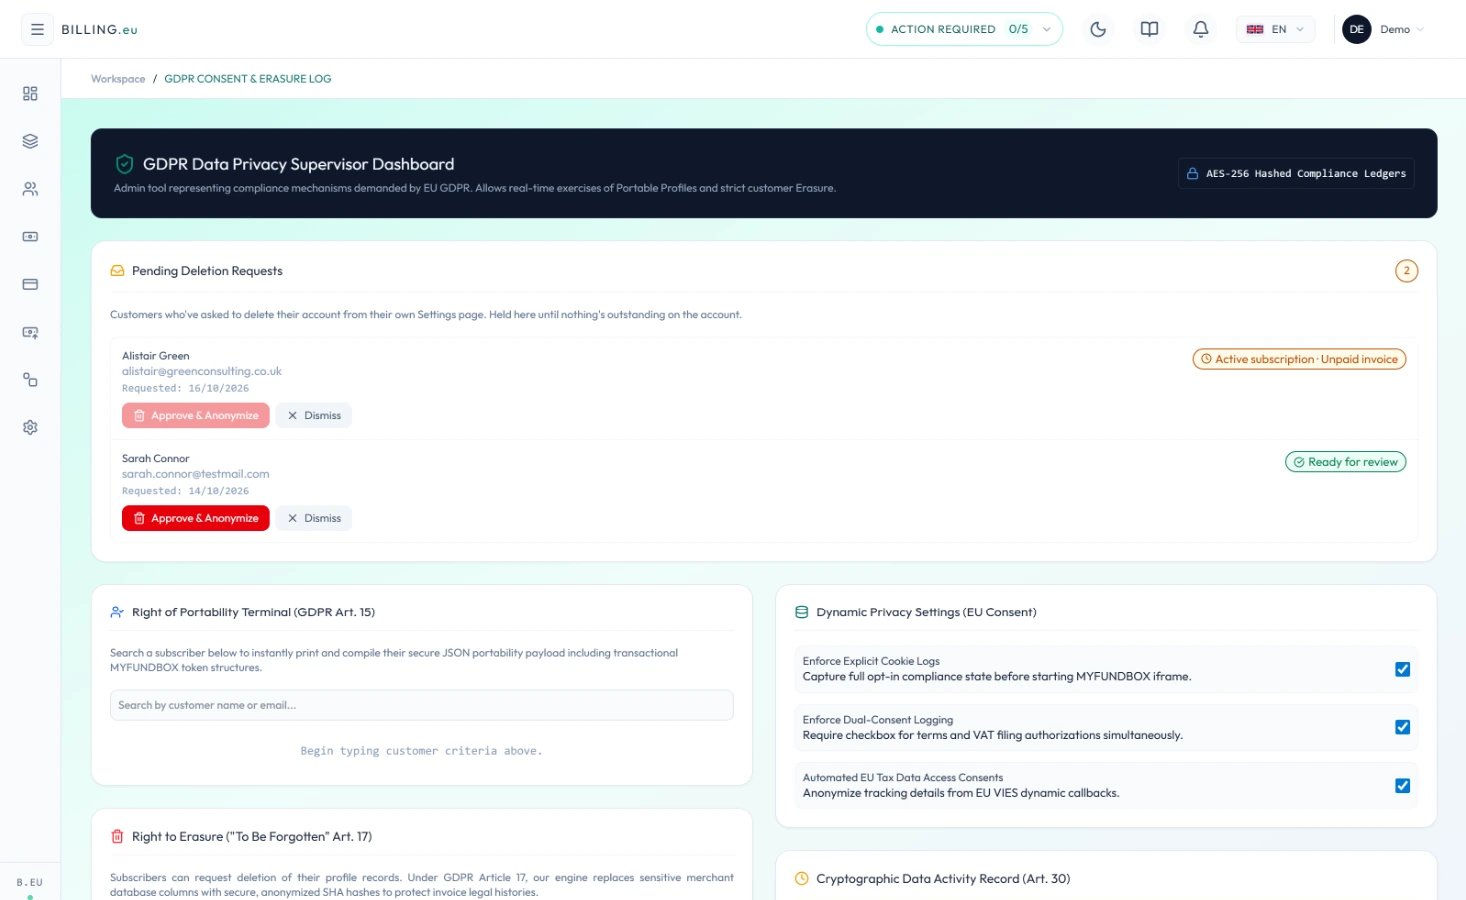
A customer's right to their own data isn't a once-a-year export. It's a working queue your team can act on.
EU GDPR Regulation 2016/679, Art. 15 & Art. 17
A customer's full profile, contract status and payment method metadata, compiled as a structured export on request.
Personal fields are scrubbed and replaced with an anonymized reference; invoice and tax records are kept, anonymized, for the retention period the law requires.
A customer can request deletion from their own account. It's held as pending, showing exactly what's still outstanding (an active subscription, an unpaid invoice), until your team reviews and approves it.
PSD2
SCA challenge flows are notoriously hard to test against a live gateway. A sandbox means your checkout is proven before launch, not during an incident.
PSD2 Regulatory Technical Standards: Strong Customer Authentication
01
Simulate a card requiring SCA at checkout.
02
Step through the authentication challenge your real customers would see.
03
Verify a successful or declined result reaches your subscription correctly.
04
Launch a checkout you've already watched handle SCA end to end.
Tax
A wrong VAT rate is a finance team's problem for months. Checking it before the invoice exists removes the problem entirely.
A customer's VAT ID is checked against the EU VIES registry as they check out, not after.
The correct rate applies automatically based on the customer's billing country, B2B reverse charge included.
E-invoicing
German e-invoicing requires structured, correct invoices. E-Invoicing checks them before they go out and keeps a record of everything that happened to them.
EN 16931 · § 14 UStG · GoBD
Required fields, structured data, VAT categories and totals are checked against EN 16931 and German rules before an XRechnung or ZUGFeRD file is generated.
Creation, validation, generation and transfer are recorded for every invoice, ready for a tax audit or your tax advisor.
Issued invoices and their audit trail stay viewable. Statutory retention under GoBD remains with your accounting system or tax advisor.
Connections to accounting software use provider-supported authentication such as OAuth 2.0. Credentials stay on the server, never in the browser.
How we protect your data
The controls that apply across Subscription Billing and E-Invoicing, written plainly, because a security page nobody can parse isn't reassuring.
Every connection to the platform, and to each payment gateway and accounting system it talks to, runs over TLS. Encryption at rest is part of the production hosting design.
Card details live with your payment gateway (Stripe, PayPal, GoCardless or Mollie). Subscription Billing stores only the token and the last four digits it needs to show you.
Each organization's data is logically separated. One organization can never read another's data, whether you run one organization or fifty.
Managed authentication with secure session handling. Passwords are never stored in plain text.
Owners, accountants and viewers only see and do what their role allows, so your tax advisor can work without full access.
Every invoice action and sign-in is recorded with the user, their role and a timestamp.
Retention can be set to match statutory archiving and deletion requirements.
Backup and recovery procedures are part of the production operations concept.
GDPR
We apply GDPR principles throughout the products and this website.
We only list certifications we actually hold. For security questionnaires or details on our controls, contact us.
Found a security issue? Email us and we’ll respond promptly.
Questions for a specific audit
We'll walk through exactly what's covered for your use case.